
How do you Outcreate cyber resilience into a business advantage in the Frontier AI era?
As AI accelerates both innovation and cyber threats, resilience can no longer be treated as a defensive imperative alone. Security leaders must connect cyber risk with business exposure, protect trust and compliance, and turn resilience into a source of competitive advantage.
LTM, in partnership with Qualys, invites you to an exclusive CISO Roundtable in Paris. This closed-door, peer-led discussion will explore how risk quantification, focused prioritization, and reduced complexity across technical data environments can help organizations Outcreate Cyber Risk Strategy into Provable Business Growth.
Organizations using this methodology are reporting an 85% improvement in vulnerability remediation time and up to a 60% reduction in mean time to remediation. Join us to explore how a more focused approach to cyber resilience can protect against disruption while enabling measurable business value.
Together, We Will Explore How Organizations Can
- Translate complex cyber threats into clear business risk exposure
- Prioritize the most critical risks without spreading resources too thin
- Use cyber resilience to protect reputation, compliance, and long-term growth

What You Will Take Away
- A clearer approach to connecting technical cyber risk with business exposure
- Practical approaches to quantifying and prioritizing the risks that matter most
- Insights into reducing complexity across technical data environments
- A stronger business case for cyber resilience as an enabler of trust, compliance, and growth
An Exclusive Peer-Led Discussion
Join fellow CISOs and cybersecurity leaders for a focused exchange of perspectives, followed by networking and dinner.
Speaker
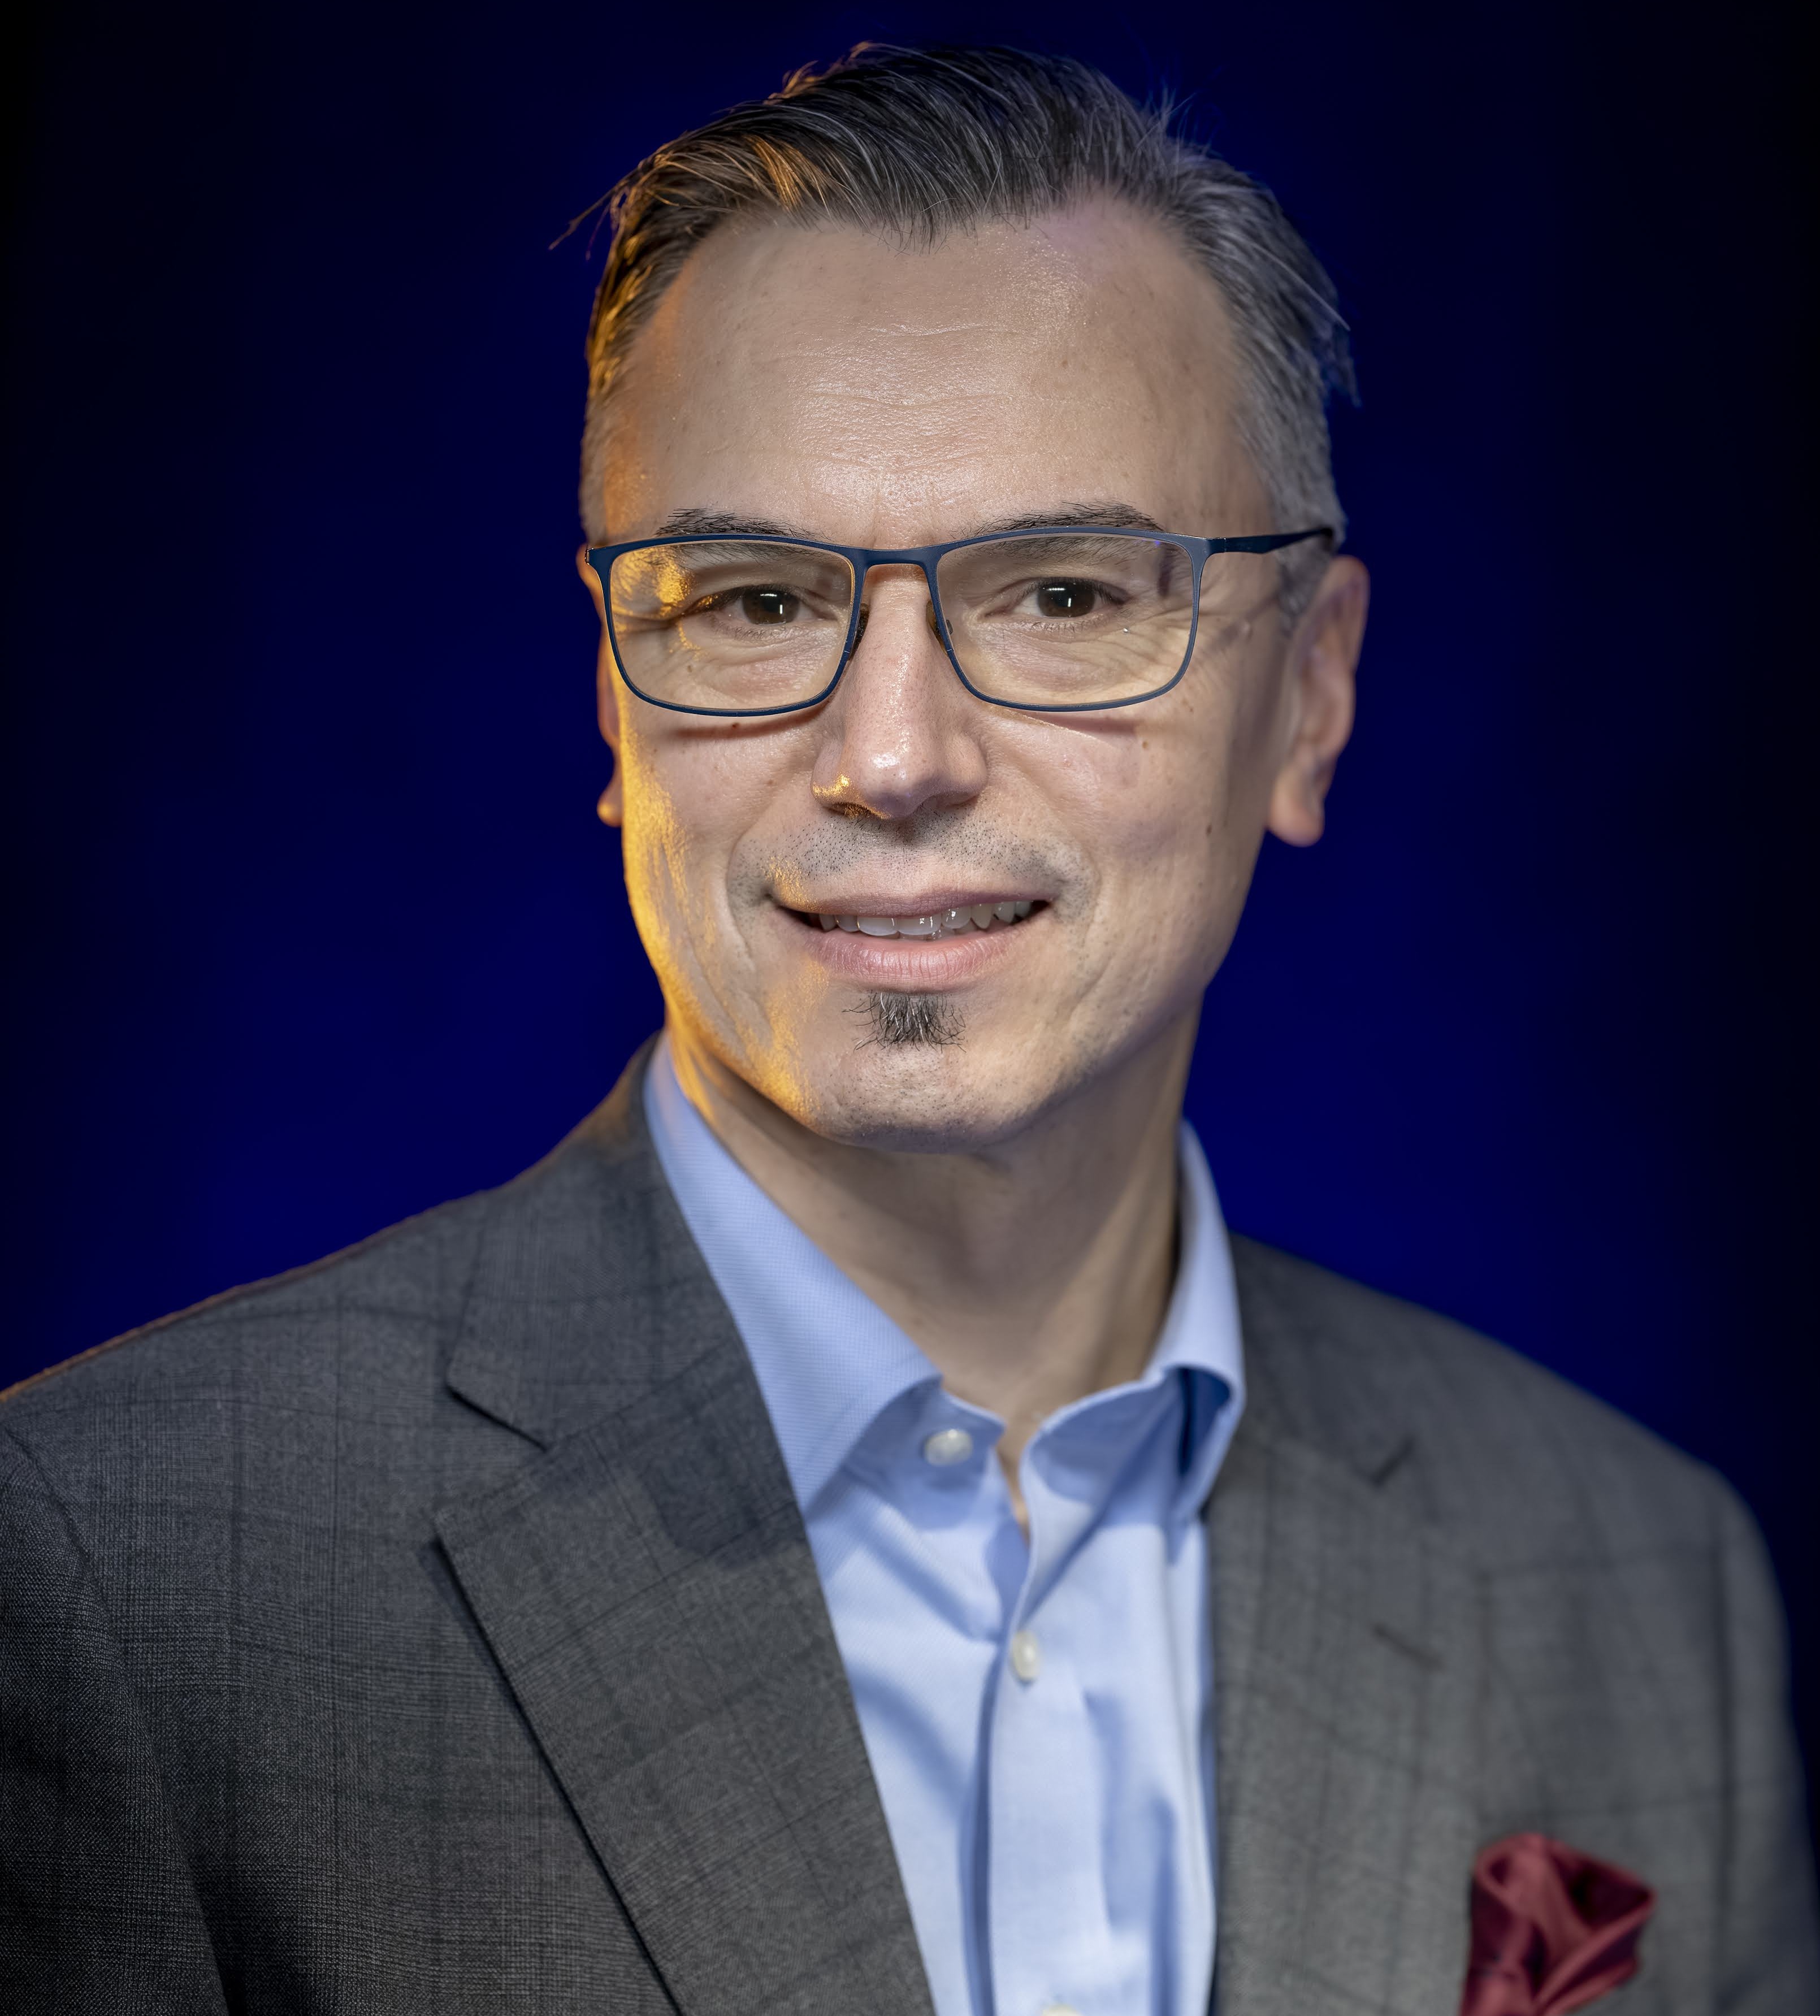
Ivan Milenkovic
Ready to translate cyber risk strategy into provable business growth?
 Outcreate Your Business
Outcreate with LTM
Outcreate Together

It’s time to Outcreate